Security and data protection
Monitoring data concerns real people in difficult places
Enterprise-grade infrastructure
- Hosted on Amazon Web ServicesAWS cloud infrastructure
- Backed by Microsoft AzureAzure cloud services
- AI assistant powered by ClaudeLarge language model by Anthropic
Controls in the platform
How access and accountability work
Data separated by contract
Each workspace holds its own projects and people, and each project its own rounds and records. Users see only the contracts they are invited to.
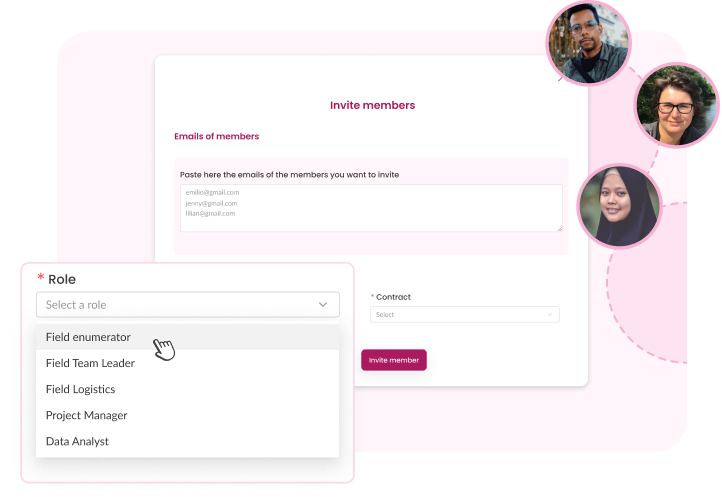
Access decided by role
Eight roles determine which menus, boards and actions are available. Field staff see their own tasks and visits.
Named, invited users
Accounts are created by invitation. Users set a password on first sign-in and confirm with a code. Admins can deactivate users at any time.
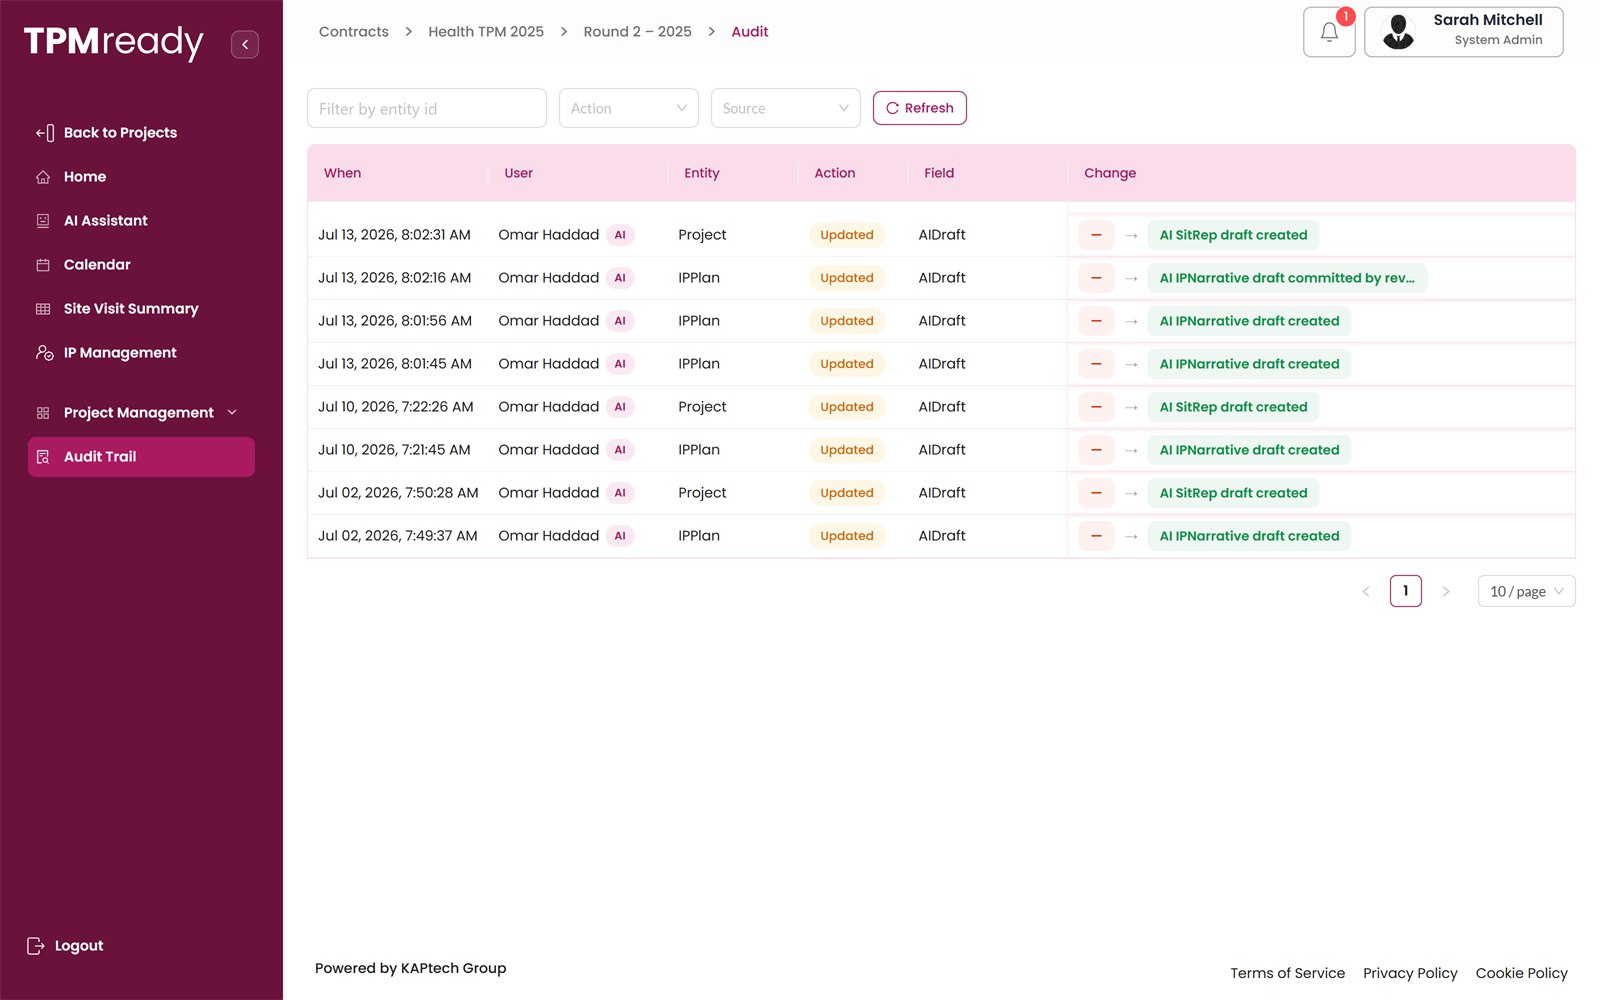
A complete audit trail
Every record created, updated or deleted is logged with old and new values, searchable by entity, action and source.
Human approval of AI output
AI drafts are reviewed, edited and accepted or discarded by a person. Nothing is saved without approval, and AI actions are marked.
Reviewed results only
Reports pass data checks and a named approval before they reach Completed. Donors receive reviewed results, not drafts.
Read-only guest access
Clients and donors can be given read-only access to selected dashboards, boards and maps.
Safeguarding as its own issue type
Safeguarding concerns are recorded as red flags with a named person responsible for follow-up and a deadline.
Field safety
Protecting enumerators and beneficiaries
Good practice we recommend
- Give guest access to dashboards and approved reports only, not to planning boards.
- Keep beneficiary identifiers out of free-text fields and flag descriptions.
- Deactivate field accounts promptly when a team member leaves the project.
- Review the audit trail at the close of each monitoring round.
For procurement and IT reviewers
Our security brief
The brief covers
- 1Data location and hosting regions
- 2Encryption of data in transit and at rest
- 3GDPR alignment and data processing terms
- 4Backup, retention and deletion on contract close
- 5Incident response and notification
- 6Certification roadmap, including ISO 27001
See also our privacy policy and terms of service.
Bring your security questionnaire
Send us your organisation's vendor or data protection questionnaire. We will complete it and walk your reviewers through the platform.